HIPAA’s biggest security rewrite in 20 years is coming, have you done your HealthData DueCare?
HIPAA, SOC 2 and ISO 27001 for covered entities and business associates, from MTC Group.
HealthData DueCare turns MTC Group’s HIPAA Compliance Checklist into a live workspace for covered entities and business associates. Every control, policy, risk, and audit is tied to a real status you can drill into, so you can prove your program holds up.
Every new account gets 24 hours of full access to the Base plan. No card required. Create your account
Why subscribe
What the platform does for your program, one module at a time.
Live HIPAA workspace
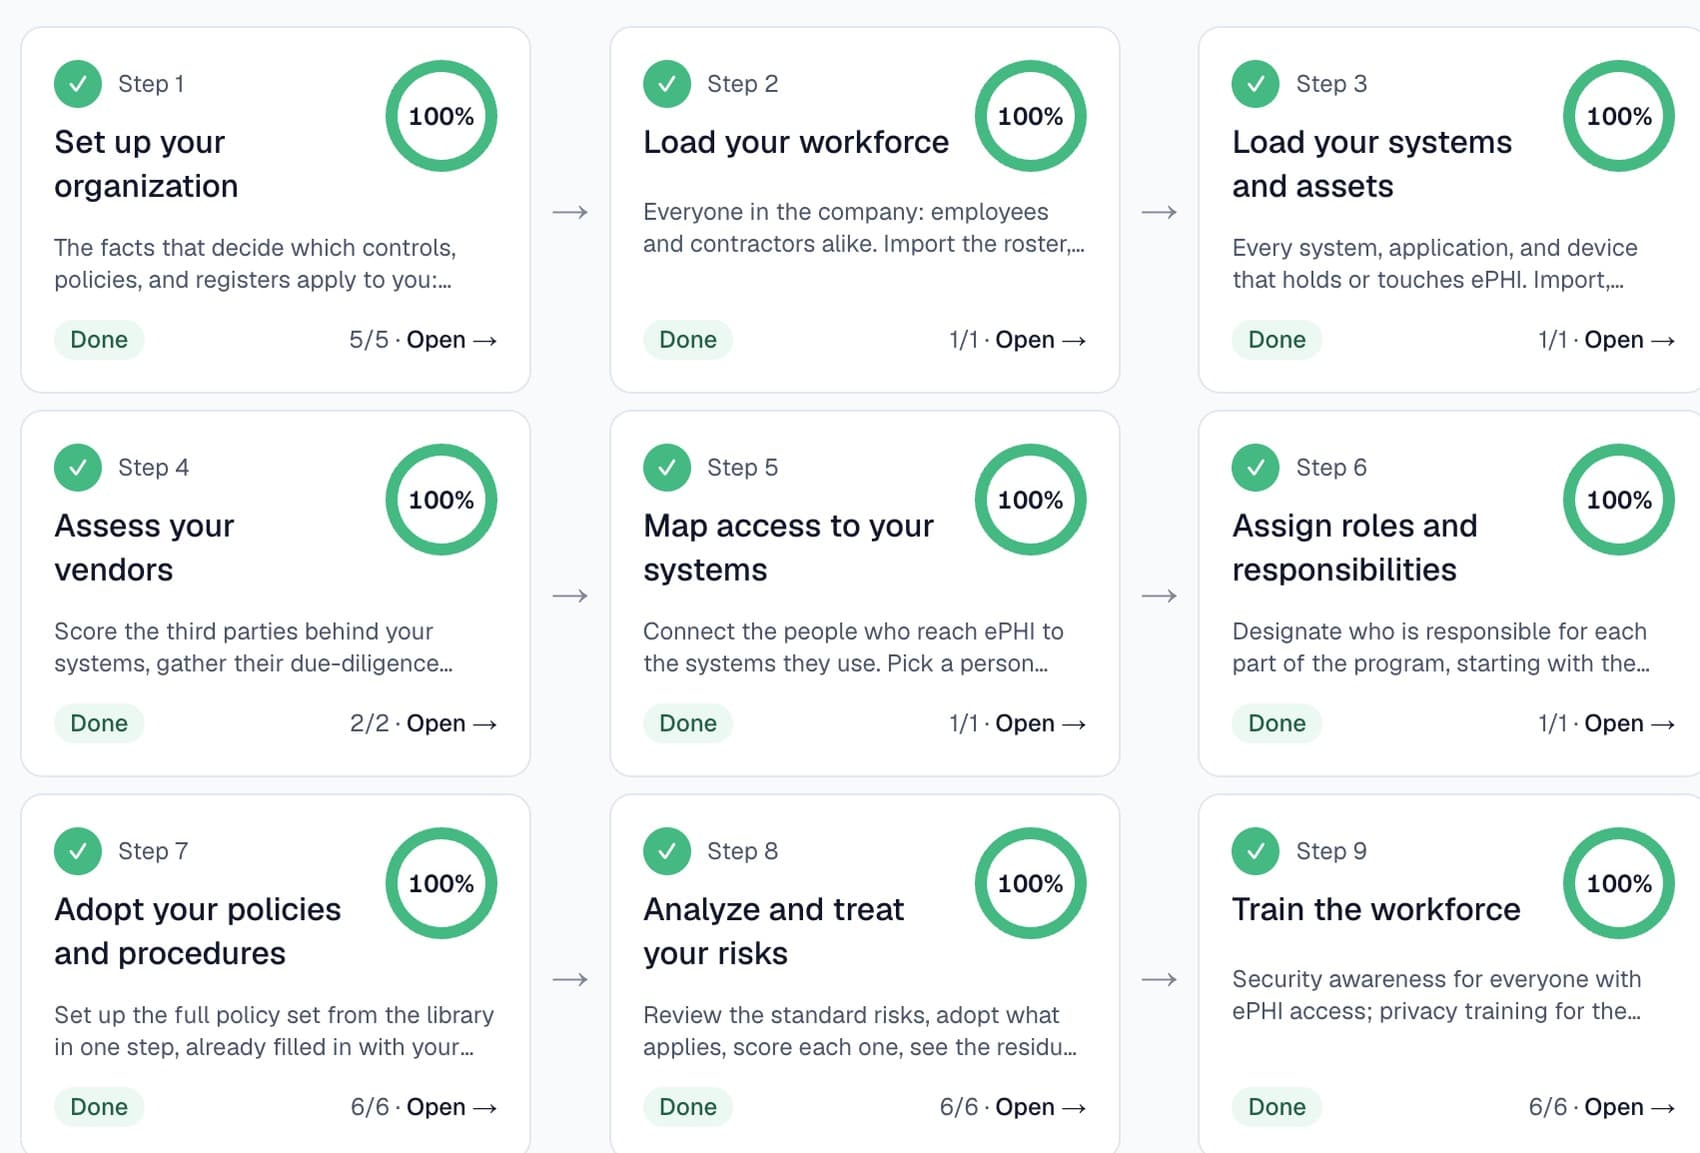
Your whole HIPAA program, step by step
The HIPAA Compliance Checklist becomes a working program: every control, policy and piece of evidence tied to a real status, broken into numbered steps you can finish one at a time.
The DueCare method
A proven method, refined since 2008, that streamlines your journey to compliance.
This is the same step-by-step approach our founder has used since 2008 to build and assess healthcare security programs. HealthData DueCare puts it in one workspace: every step in order, each tied to the controls and evidence underneath it, so you always know what is done and what comes next.
Here are the Domains Necessary to
Demonstrate OCR’s Required HIPAA Due Diligence/Due Care
The full HIPAA Security Rule checklist, readable domain by domain, the same real citations that power the live platform. Click a domain to read it now, or see the whole guide.
Plus the full NIST Cybersecurity Framework 2.0 crosswalk, mapped from the same checklist data. Create a free account to explore it. Want a printable copy? Print the full checklist as a PDF (free account required).
What makes HealthData DueCare different
Built for organizations without a security department
Health tech startups, the nonprofits handling health data beside them, practices with fewer than ten physicians, and rural and community hospitals. Designed for them deliberately, not scaled down from enterprise software.
Command of a real program, not security theater
One place that holds the whole program: controls, risks, vendors, training, evidence, and who owns each part, tied together rather than scattered across spreadsheets nobody reconciles. And none of what it holds is your patients' data.
A living program, not an annual scramble
Evidence is produced as the program runs, not assembled the month before an audit. Compliance becomes a strategic asset you can show a customer on any given day.
Two HIPAA programs, and why we recommend NIST
The OCR minimum is a self-attestation. The NIST program carries every standard to NIST SP 800-66 Rev. 2 and can earn an independent RSP report, the record regulators, customers and insurers give weight to.
One pathway from HIPAA to SOC 2 and ISO 27001
Set a HIPAA baseline first, then mature into the certification frameworks on top of it. The baseline work carries forward instead of being rebuilt.
Less than half the cost, in months rather than years
Comparable platforms run $10,000 to $30,000 a year for a single framework. This one starts at $349 a month, with a program built in three to six months rather than a multi-year effort.
Cancel your platform subscription any time
No multi-year licence and no lock-in. The platform subscription is month to month, and you cancel it yourself from the Billing page without calling anyone.
Every citation, sourced, and flagged before it changes
Every control cites its real 45 C.F.R. section with a live source link, and flags what OCR's pending 2025 rule would make mandatory.
Scoped to your actual role, not a one-size-fits-all checklist
Built for Business Associates and the real obligations a BAA creates, with a Covered Entity layer (Domain L) for organizations that also carry their own direct Privacy Rule duties.
Included with every platform plan
InfoSec Signals, at no extra cost
CVEs matched to the systems you record here, the vulnerabilities attackers are exploiting now, breaches and lessons from organizations like yours, and the HHS rules that apply to you, with a weekly digest built around your program. For your site administrator, a $5/month value.
Beyond the free checklist
Buy a template pack outright, or subscribe for live platform access, for HIPAA and for SOC 2 or ISO/IEC 27001, with MTC Group fCISO support at the level you need.
DIY template packages
Buy the documents outright and run the program yourself, offline. One-time, no subscription.
HIPAA Template Packs (BA and CE)
The full HIPAA template packet, for an OCR minimum or a NIST program, for total self-service, self-attestation use, offline, with no platform subscription (an independent RSP report needs a NIST program on the platform). Two editions: Business Associate (Domains A through K) and Covered Entity (adds Domain L, the Privacy Rule patient-rights set).
SOC 2 and ISO 27001/2 Template Packs
Do-it-yourself packs for the next level after HIPAA, one pack each for covered entities and business associates alike, built on the HIPAA program they include.
Platform subscriptions
The live platform: your program, registers, training and evidence in one place, with your Trust Hub.
HIPAA Platform: Base
Full platform access for your HIPAA program, on the OCR minimum or NIST. The Recognized Security Practices Assessment is available separately, for NIST programs.
SOC 2 or ISO 27001/2 Platform (DIY)
The platform with your SOC 2 or ISO 27001/2 program added to your HIPAA program, with the evidence you already have carried across. Added once your HIPAA program is filed and your RSP Assessment is issued, which is also the cheaper order to do it in.
RSP Assessment, InfoSec Advisor and fCISO
Your Recognized Security Practices Assessment by an independent RSP Assessor, an InfoSec Advisor to coach your own team, or an fCISO to lead your program.
Recognized Security Practices Assessment
For NIST programs: an independent RSP Assessor's assessment of your filed HIPAA attestation, including a 1-hour virtual interview, findings, and a signed RSP Assessment Report.
InfoSec Advisor (add-on)
For organizations whose own team will do the work and wants a certified professional in its corner: someone who reviews your program, answers your questions and coaches the next step on HIPAA, SOC 2 or ISO 27001. The advisor guides; your team builds. The advisor is not your organization's designated security professional.
fCISO Retainer (add-on)
For organizations with no professional security staff: no CISO, security officer or security analyst on the payroll. If you already have one, your platform plan is all you need. An add-on to your platform subscription: MTC Group's fractional CISO leading your HIPAA, SOC 2 or ISO 27001/2 program, through to the auditor where there is one.
Every new account gets 24 hours of full access to the Base plan. No card required.
Why we built HealthData DueCare
61 million
people affected by reported healthcare breaches in 2025 alone
$7.42M
average cost of a US healthcare breach, the costliest industry 14 years running
279 days
to identify and contain a healthcare breach once it starts
16 settlements
from OCR between January and August 2025, every one citing no accurate, thorough risk analysis
Health technology startups, the nonprofit organizations that handle health data alongside them, and small covered entities, practices with fewer than ten physicians and rural and community hospitals, all carry a health system’s HIPAA obligations without a health system’s staff or budget. The regulator is pointed straight at that gap: OCR’s Risk Analysis Initiative has targeted smaller organizations since 2024, and penalties scale with size while the expectations do not. HHS puts the first-year cost of its proposed Security Rule overhaul at $9 billion for the industry, and $33 billion over five years.
I spent years building these programs myself, then assessed them for DirectTrust and EHNAC, and later guided organizations in exactly this market through SOC 2 assessments as an independent consultant. The same thing happened every time: the work cost far more, and took far longer, than it needed to. A consultant rebuilds the same policy set, the same risk analysis and the same evidence trail for every client, bills for the rebuild, and leaves the organization with a binder rather than a program that keeps running.
HealthData DueCare exists to close that gap. The platform and the fractional CISO services behind it are built to prove HIPAA compliance and carry an organization to the next level, SOC 2 or ISO/IEC 27001, within three to six months and for less than half of what that path normally costs, with the evidence produced as the program runs rather than assembled the month before an audit.
Rick A. Moore, Founder and CEO, MTC Group LLC
Who’s behind this
Rick A. Moore, , , , , , ,
Founder & CEO, MTC Group
Built by a healthcare information security executive, not an anonymous content pipeline. As CIO/CISO at NCQA, Rick designed and deployed a certified ISO/IEC 27001 information security management program that sustained more than a decade of external audits without a single non-conformity. His consulting practice has built and assessed SOC 2 and ISO 27001 compliance programs for healthcare organizations, and he previously served as an auditor for DirectTrust.
He has also led health informatics for a 200+ hospital network, built EHR systems within the DoD Office of the Secretary of Defense, and served as adjunct faculty at four universities, including Hofstra University’s graduate healthcare privacy, security, and informatics program and Virginia Commonwealth University’s PhD-level health informatics program. Every control and template here reflects someone who has actually carried the accountability HIPAA compliance programs are audited against, not a generic template library assembled by someone who has never run one.
Connect with Rick on LinkedIn →